Autor Cointelegraph by Zoltan Vardai

Crypto hackers stole $17B over past 10 years: DefiLlama

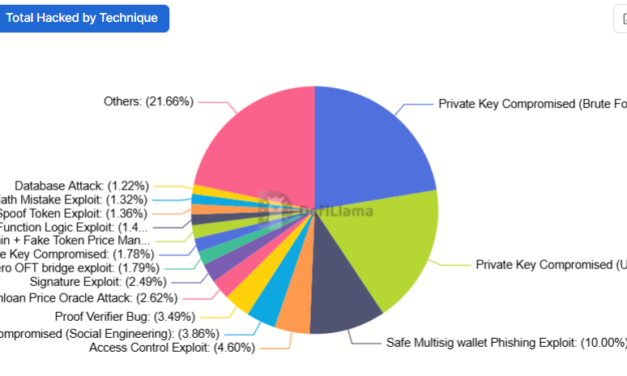
Private key compromises are emerging as one of crypto’s costliest attack vectors, with hackers stealing more than $17 billion across 518 recorded incidents over the past decade, according to data platform DefiLlama.In data shared Tuesday, DefiLlama’s dashboard shows a large share of those incidents stemmed from compromised private keys, alongside phishing and other credential-based attacks.Total hacked by the technique. Source: DefiLlama Around 22.3% of the incidents were attributed to private key compromises through “brute force,” 18.2% to private key compromises via “unknown methods,” and 10% occurred due to phishing attacks on multi-signature wallets. The figures add to evidence that some of the industry’s biggest losses are increasingly coming from weaknesses in wallet security, signing infrastructure and user behavior, rather than from flaws in protocol code alone.The findings come days after the crypto industry suffered its largest hack so far in 2026 on Saturday, when an attacker drained about 116,500 restaked Ether (rsETH), worth roughly $290 million to $293 million at the time, from Kelp DAO’s LayerZero-powered rsETH bridge.Source: DefiLlamaDeFi protocols lost $600 million in two months: GSR ResearchThe recent wave of losses has also hit decentralized finance hard. More than $600 million was stolen from DeFi protocols over the past 60 days, according to a Monday report from crypto trading company GSR, with the Kelp exploit and the April 1 exploit involving Solana-based decentralized exchange Drift Protocol accounting for most of the total.The attacks are raising new questions about whether improving smart contract audits alone is enough to protect users. In its report, GSR said attackers appear to be shifting toward “operational security, signing infrastructure, developer tooling, and the humans behind them” as smart contract security continues to improve.That shift is pressuring a sector already facing narrower returns. “DeFi yields have compressed toward TradFi rates, raising the question of whether depositing onchain is still worth the risk,” GSR wrote.Major DeFi exploits. Source: GSR Research“Lazy” hacks are spreading due to AI and malwareCybersecurity companies say advances in malware and artificial intelligence are making social engineering and wallet-targeting attacks easier to scale, which involve scammers tricking victims into sending crypto to illicit addresses by first sending them small transactions, hoping that investors copy and paste the attacker’s address from the transaction history.Related: ZachXBT asks MemeCore to explain valuation and token supplyThe rise of hacking-as-a-service tools is also lowering the barrier to entry for would-be attackers, according to Dyma Budorin, co-founder and CEO of cybersecurity firm Hacken.“If people are getting these links, their wallets can be completely drained,” Budorin told Cointelegraph in an interview at EthCC 2026. “The platform on the darknet will take the commission for their tools and [scammers] get the bigger portion of the drained wallets.”Budorin added that hackers are usually seeking out the easiest targets that require the least effort to scam.Dyma Budorin, co-founder and CEO at Hacken, interview at EthCC 2026. Source: CointelegraphWeb3 projects lost $482 million in the first quarter of 2026, as phishing and social engineering scams drove $306 million of those losses as the largest attack vector, according to a report by Hacken.Even so, some parts of the threat picture have improved. Scam Sniffer said in a January report that losses tied to crypto phishing attacks fell sharply in 2025, suggesting users were becoming more aware of the threat, even as wallet-drainer scripts and new malware strains continued to circulate.Magazine: 53 DeFi projects infiltrated, 50M NEO tokens could be ‘given back’: Asia ExpressCointelegraph is committed to independent, transparent journalism. This news article is produced in accordance with Cointelegraph’s Editorial Policy and aims to provide accurate and timely information. Readers are encouraged to verify information independently. Read our Editorial Policy https://cointelegraph.com/editorial-policy

Čítaj viac
Kelp DAO attacker moves $175M in Ether after exploit: Arkham

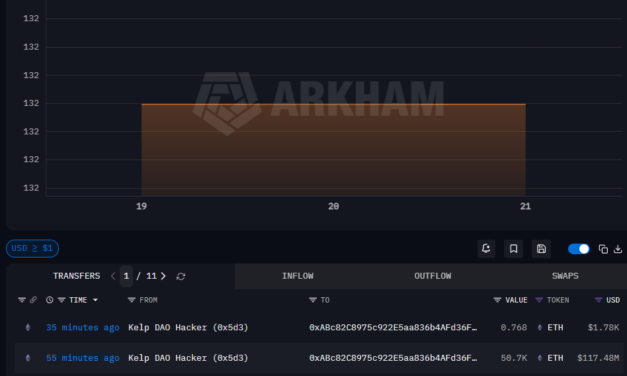
The attacker behind the roughly $290 million Kelp DAO exploit began moving tens of thousands of Ether to newly created blockchain addresses on Tuesday, in an apparent effort to start laundering the stolen funds.The wallet tagged by Arkham as linked to the Kelp DAO exploit moved about 75,700 Ether (ETH) worth roughly $175 million across three transactions on Tuesday, including a 25,000 ETH transfer to one newly created address and transfers of 50,700 ETH and 0.7 ETH to another.Blockchain investigator ZachXBT wrote in a Tuesday Telegram post that addresses tied to the exploit had begun moving funds through THORChain and Umbra. He flagged three THORChain transactions totaling about $1.5 million and a separate $78,000 transfer through Umbra.On Saturday, an attacker drained about 116,500 restaked Ether (rsETH), worth roughly $290 million to $293 million at the time, from Kelp DAO’s LayerZero-powered rsETH bridge.LayerZero said Kelp DAO’s 1/1 decentralized verifier network (DVN) setup created a single point of failure by relying on a single verifier path for cross-chain messages. LayerZero said it had previously advised against that configuration.Fallout spreads across DeFiThe transfers came hours after Arbitrum said its 12-member security council had taken emergency action to freeze 30,766 ETH tied to the exploit and move the funds into an “intermediary frozen wallet” accessible only through Arbitrum governance.Kelp DAO attacker-tagged wallet, latest transactions. Source: Arkham The exploit also hit other DeFi protocols, including Aave, where the attacker used the stolen funds as collateral to borrow against the protocol. Early estimates put the hole at about $195 million, but Aave’s Monday incident report later outlined two potential outcomes: roughly $123.7 million in bad debt under one scenario and about $230.1 million under another.The transfers suggest the attackers had begun moving funds through non-custodial protocols that can complicate tracing and recovery. THORChain does not require traditional Know Your Customer checks.During the $1.4 billion Bybit hack in 2025, attackers converted about 83% of the stolen Ether into Bitcoin (BTC), with 72% of the funds moving through THORChain, according to Bybit CEO Ben Zhou. Zhou said at the time that 77% of the stolen funds were still traceable.Related: ZachXBT asks MemeCore to explain valuation and token supplyAave unfreezes Ethereum V3 market as borrow rates spikeOn Tuesday, Aave said it had unfrozen Wrapped Ether (WETH) reserves on the Ethereum Core V3 market, enabling users to supply WETH to the V3 lending protocol once again. However, WETH reserves across Ethereum Prime, Arbitrum, Base, Mantle and Linea remain frozen.Source: Julio MorenoMeanwhile, the thinning liquidity saw Aave’s borrowing rates for USDt (USDT) rise from 3% to 14%, marking the highest figures since December 2024, wrote Julio Moreno, the head of research at analytics platform CryptoQuant, in a Monday X post.Fears over a potential contagion caused significant outflows from Aave, as its total value locked (TVL) fell by about $10 billion since the exploit to $16.4 billion as of Tuesday, DefiLlama data shows.Magazine: 53 DeFi projects infiltrated, 50M NEO tokens could be ‘given back’: Asia ExpressCointelegraph is committed to independent, transparent journalism. This news article is produced in accordance with Cointelegraph’s Editorial Policy and aims to provide accurate and timely information. Readers are encouraged to verify information independently. Read our Editorial Policy https://cointelegraph.com/editorial-policy

Čítaj viac
ZachXBT asks MemeCore to explain valuation and token supply

Onchain investigator ZachXBT publicly challenged MemeCore on Monday to justify the valuation and supply distribution of its M token, asking the project to explain its market cap and why “insiders hold >90% of supply.”“Please provide a single data point to support your $6B mkt cap at a top 20 token and why insiders hold >90% of supply,” wrote ZachXBT in a Monday X response to Memecore, a project advertising itself as the layer–1 blockchain for the “Meme 2.0 economy.”The comments add fresh scrutiny to MemeCore after a sharp rally, though live valuation metrics differed across major trackers. CoinMarketCap ranked the token No. 21 at about $4.33 billion on Monday, while CoinGecko ranked it No. 20 at about $5.97 billion.Bubblemaps showed concentrated M token holdings, with wallet “0x8b8” holding 50 million tokens worth about $178 million and a Binance deposit address appearing as the largest visible holder. But Bubblemaps analyst 0xToolman told Cointelegraph the pattern looked more like team-held allocations than evidence of coordinated trading, adding that some of those tokens may not yet be in circulation.M token, top 250 holders by amount. Source: BubblemapsCointelegraph has contacted MemeCore for comment on the matter and details surrounding the token’s distribution.ZachXBT has not posted definitive blockchain data proving that 90% of the supply is held by insiders, but pledged to investigate the token after the recent meltdown of the Rave DAO (RAVE) token sent shockwaves across the industry.Related: Suspected insider wallets rack up $1.2M betting on ZachXBT’s Axiom exposéRAVE token’s 90% meltdown sparks insider concernsOn Saturday, ZachXBT accused RaveDAO of orchestrating a pump-and-dump scheme, citing concentrated token holdings and suspicious exchange flows, after the RAVE token soared from $0.25 to nearly $28 within days before crashing over 80%.RaveDAO has denied any role in the token’s surge and collapse, Cointelegraph reported on Sunday. Both Binance and Bitget confirmed they are reviewing the situation.The RAVE token fell 92% during the past week and was trading above $0.69 at 12:46 p.m. UTC on Monday, CoinMarketCap data shows.RAVE/USD, 1-year chart. Source: CoinMarketCapZachXBT claimed that RAVE was just one of several tokens spotting “manipulation” signs on major exchanges.“Other projects with highly questionable price action recently include: SIREN, MYX, COAI, M, PIPPIN, RIVER,” he wrote in a Saturday X post, pledging to investigate these price movements to identify the responsible parties.Magazine: Meet the onchain crypto detectives fighting crime better than the copsCointelegraph is committed to independent, transparent journalism. This news article is produced in accordance with Cointelegraph’s Editorial Policy and aims to provide accurate and timely information. Readers are encouraged to verify information independently. Read our Editorial Policy https://cointelegraph.com/editorial-policy

Čítaj viac
Získaj BONUS 8 € v Bitcoinoch

nakup bitcoin z karty

Registrácia Binance

Burza Binance

Aktuálne kurzy