Autor Cointelegraph by Zoltan Vardai

Solana more than triples transaction size limit with mainnet upgrade

Solana raised its maximum transaction size from 1,232 bytes to 4,096 bytes to allow developers to fit more complex operations into a single transaction, including zero-knowledge proofs and new onchain signature schemes.The upgrade was activated on mainnet on Tuesday at the start of epoch 1,035 around 1:00 am UTC, according to blockchain data shared by the Solana Foundation.The upgrade also introduced the v1 transaction format, which maintains full backward compatibility with legacy transactions. Existing transaction formats continue working for applications and wallet providers, but protocols that want to benefit from the size increase need to update to v1 transactions.A spokesperson for the Solana Foundation told Cointelegraph that the upgrade mainly aims to help developers “do more” with applications such as zero-knowledge proofs, transactions requiring multiple signatures and new onchain signature schemes, by unlocking workloads that previously couldn’t fit inside a single transaction.In August, Solana reduced its slot time from 400 milliseconds to 350ms. In June, the Solana Foundation shared plans to reduce slot times from 400ms to 200ms, arguing that it would improve latency and accelerate confirmations on the blockchain network.Solana validators approved on Aug. 28 a proposal to double the network’s annual disinflation rate, reducing future issuance of Solana (SOL), the network’s native token.Related: Solana sees record 263K tokens issued in a single dayCointelegraph is committed to independent, transparent journalism. This news article is produced in accordance with Cointelegraph’s Editorial Policy and aims to provide accurate and timely information. Readers are encouraged to verify information independently.

Čítaj viac
Fragmented regulations limit stablecoin adoption in international finance: WTO head

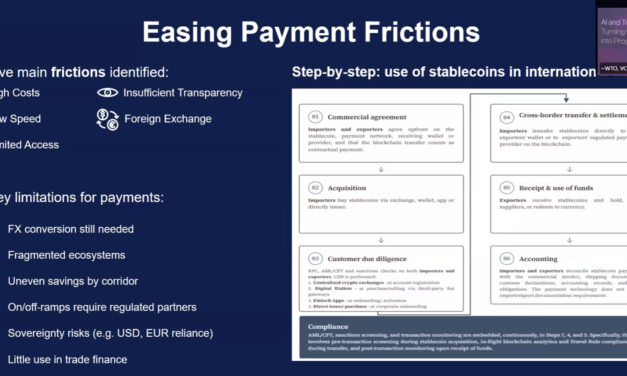
Fragmented regulatory regimes are limiting stablecoin adoption in international trade, according to Juan Marchetti, director of the trade in services and investment division at the World Trade Organization (WTO).“The constraint is not technology. It is actually regulation and the lack of development of regulatory frameworks,” said Marchetti during a Monday speech in Geneva, at the launch of WTO’s study on stablecoins in world trade.He cited an October 2025 report from the Financial Stability Board which found that only 39%, or 11 out of 28 surveyed jurisdictions, have finalized their stablecoin regulatory frameworks.Marchetti added that stablecoins may improve some of the main friction points of trade finance, but currently only account for 3% of total international payments due to fragmented regulatory regimes. The WTO’s report identified five friction points that may be improved by stablecoin adoption, including high costs, low speed, limited access, insufficient transparency and foreign exchange limitations.Stablecoins ability to ease friction in international payments. Source: Cointelegraph/WTOThe report also revealed that stablecoin payments in cross-border payments grew 35-fold between 2020 and mid-2024.Related: Metaplanet cuts Series 10 stock pool by 41%, plans Hong Kong subsidiaryEmerging economies stand to gain most from stablecoin adoption: WTODeveloping economies stand to benefit most from stablecoin adoption due to their ability to reduce remittance fees. However, these same countries have the least developed regulatory regimes to facilitate adoption, according to the WTO’s director. He said:“Contribution to trade will depend far less on the technology than on regulatory convergence, interoperability and the surrounding financial infrastructure, especially in developing economies that stand to gain.”Some of the largest global payment processors are exploring stablecoins to improve cross-border payments.In August, Mastercard partnered with stablecoin orchestration network Borderless to pilot how to bring more trust into cross-border stablecoin transfers through the payment processing giant’s Crypto Credential framework. In June, it announced plans to expand its settlement capabilities to include intraday, weekend and holiday card settlement, including settlement through stablecoins.Also in August, Western Union said it partnered with stablecoin infrastructure provider Rain to launch a digital wallet and Visa-branded card that enables users to hold and spend a US dollar-backed stablecoin in 37 markets, planning to expand it to more than 60 markets by the end of the year.Magazine: Why Australia’s $17B crypto opportunity depends on regulation

Čítaj viac

EU cyber rules put crypto wallet makers on 24-hour reporting clock

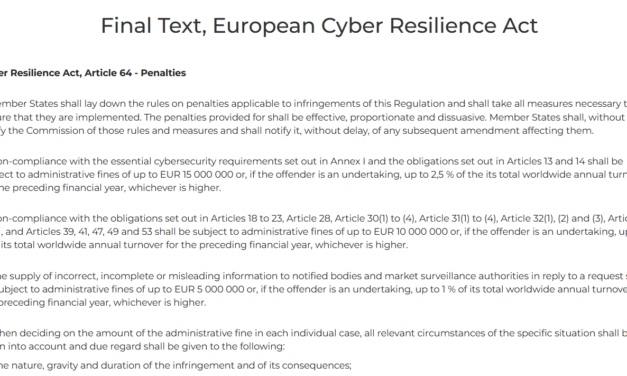
The EU is telling cryptocurrency hardware and software wallet providers that they have 24 hours from awareness to report actively exploited bugs or severe security vulnerabilities affecting their products.The measure is part of the EU’s Cyber Resilience Act (CRA), which took effect on Friday, according to an announcement from the European Commission.Manufacturers must submit an early warning for severe vulnerabilities within 24 hours, followed by a full notification within 72 hours. A final report will be required 14 days after corrective or mitigating measures are available and within one month for severe incidents.The EC said the new reporting requirements aim to better protect consumers and businesses from cyber threats. The measure extends to all products “with digital elements made available in the EU” and builds on the EU’s broader cybersecurity strategy.Cointelegraph has approached the European Commission for more details surrounding the cybersecurity measures.Related: German finance ministry proposes 25% crypto tax starting 2028: ReportFines could reach $17 millionCompanies that fail to adhere to the cybersecurity measures under Articles 13 and 14 may face an administrative fine of up to 15 million euros ($17.3 million) or 2.5% of worldwide annual turnover, depending on which figure is higher, according to the penalties section of the final draft.Supplying incorrect, incomplete or misleading information will also subject companies to an administrative fine of up to 5 million euros.Excerpt from Final Text, European Cyber Resilience Act. Source: European-Cyber-Resilience-Act.com The measure was revealed weeks after two popular hardware wallet providers disclosed user data breaches that could lead to phishing or social engineering attempts. On Sept. 4, hardware wallet provider Trezor revealed that an additional 67,000 US customers were at risk from the data breach suffered by its shipping provider, ShipMonk, exceeding the initially estimated 14,000 users.On Wednesday, Trezor and BitBox warned users about phishing emails disguised as urgent security notices after suspected compromises involving third-party email services.  In June, Layer-1 blockchain network Zilliqa warned that a vulnerability in the Zilliqa Ledger app could allow attackers to recover users’ private keys using publicly available onchain data.Cointelegraph has approached wallet makers Trezor and Ledger for comment on how wallet providers would comply with the new reporting requirements.Magazine: How Hong Kong is turning tokenized bonds into real market infrastructure

Čítaj viac

Symbiosis says recovered 15 BTC from bridge hack, offers 20% bounty

Cross-chain liquidity protocol Symbiosis said it recovered 15 Bitcoin, worth around $1.1 million, from a Bitcoin bridge exploit it suffered Friday.Symbiosis said it recovered 15 Bitcoin (BTC) into a team-controlled multi-sig wallet and clarified that all routes remain operational, according to a Friday X post. The exploit affected Symbiosis’ native Bitcoin bridge, which remains paused.The attacker’s address minted 46.1 billion unbacked tokens from the protocol’s Bitcoin bridge but realized net proceeds of 4.3 Wrapped Bitcoin (WBTC), worth $336,000, according to blockchain security company Blockaid, which flagged the exploit on Friday. The protocol has not specified how the recovered Bitcoin relates to the $336,000 in proceeds attributed to the attacker.Symbiosis is now offering a 20% bounty to anyone who provides information that leads to asset recovery. The protocol initially offered a 20% white-hat bounty for the attacker to return the funds, but the deadline expired on Sunday. The protocol said it will reveal a compensation framework for affected liquidity providers.DefiLlama clocked around $336,000 lost in the exploit, but the protocol has yet to disclose its final accounting of losses incurred.Bridge exploits continue testing DeFiIn June, Secret Network suffered an “infinite mint” exploit that drained about $4.6 million from the protocol.In May, the Verus-Ethereum bridge was drained in a forged cross-chain transfer exploit for 5,402 Ether, then worth about $11.6 million. The hacker returned 75% of the stolen funds and kept about 1,350 Ether, or $2.8 million, a day after the protocol offered it a 25% white-hat bounty.Related: Anthropic says Claude used for cyberattacks and surveillanceCointelegraph is committed to independent, transparent journalism. This news article is produced in accordance with Cointelegraph’s Editorial Policy and aims to provide accurate and timely information. Readers are encouraged to verify information independently.

Čítaj viac
Symbiosis says recovered 15 BTC from bridge hack, offers 20% bounty

Cross-chain liquidity protocol Symbiosis said it recovered 15 Bitcoin, worth around $1.1 million, from a Bitcoin bridge exploit it suffered Friday.Symbiosis said it recovered 15 Bitcoin (BTC) into a team-controlled multi-sig wallet and clarified that all routes remain operational, according to a Friday X post. The exploit affected Symbiosis’ native Bitcoin bridge, which remains paused.The attacker’s address minted 46.1 billion unbacked tokens from the protocol’s Bitcoin bridge but realized net proceeds of 4.3 Wrapped Bitcoin (WBTC), worth $336,000, according to blockchain security company Blockaid, which flagged the exploit on Friday. The protocol has not specified how the recovered Bitcoin relates to the $336,000 in proceeds attributed to the attacker.Symbiosis is now offering a 20% bounty to anyone who provides information that leads to asset recovery. The protocol initially offered a 20% white-hat bounty for the attacker to return the funds, but the deadline expired on Sunday. The protocol said it will reveal a compensation framework for affected liquidity providers.DefiLlama clocked around $336,000 lost in the exploit, but the protocol has yet to disclose its final accounting of losses incurred.Bridge exploits continue testing DeFiIn June, Secret Network suffered an “infinite mint” exploit that drained about $4.6 million from the protocol.In May, the Verus-Ethereum bridge was drained in a forged cross-chain transfer exploit for 5,402 Ether, then worth about $11.6 million. The hacker returned 75% of the stolen funds and kept about 1,350 Ether, or $2.8 million, a day after the protocol offered it a 25% white-hat bounty.Related: Anthropic says Claude used for cyberattacks and surveillanceCointelegraph is committed to independent, transparent journalism. This news article is produced in accordance with Cointelegraph’s Editorial Policy and aims to provide accurate and timely information. Readers are encouraged to verify information independently.

Čítaj viac
Získaj BONUS 8 € v Bitcoinoch

nakup bitcoin z karty

Registrácia Binance

Burza Binance

Aktuálne kurzy