Autor Cointelegraph By Helen Partz

MiCA focus shifts from rulemaking to supervision, ESMA chair says

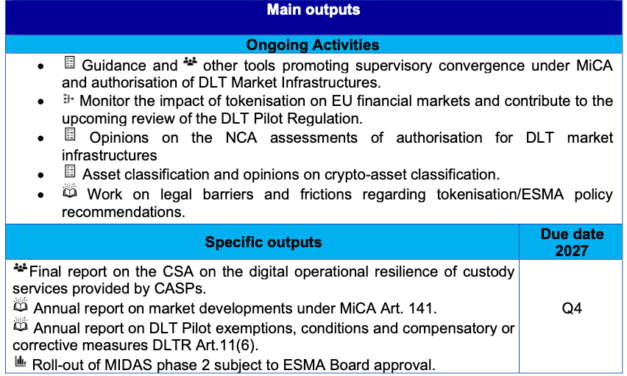
The European Securities and Markets Authority (ESMA) will focus its coordination of national crypto supervision in 2027 on operational resilience, outsourcing and firms maintaining sufficient operations inside the bloc as implementation deepens under the Markets in Crypto-Assets Regulation (MiCA).ESMA Chair Verena Ross said Monday that the regulator’s focus under MiCA had shifted “from rulemaking towards supervision and convergence.”“We want innovation to flourish within a framework that provides clarity for firms, safeguards for investors and confidence in the markets,” Ross said during a meeting of the European Parliament’s Committee on Economic and Monetary Affairs.ESMA set out the priorities in its 2027 work program, published Monday. The regulator plans to strengthen coordination among national regulators supervising crypto asset service providers (CASPs), with operational resilience, outsourcing risks, liquidity, reverse solicitation and asset classification among its areas of focus.ESMA also intends to harmonize CASPs’ periodic reporting to national regulators and promote common risk indicators and supervisory dashboards. ESMA plans to advance MIDAS, its centralized crypto-market surveillance system for monitoring potential market abuse under MiCA.Source: ESMAThe regulator expects the system’s first phase to be fully operational in 2027. ESMA previously disclosed plans for a second phase in February. Monday’s work program said it would add analytical features and expand the types of data available, with rollout scheduled for the fourth quarter subject to board approval.ESMA also plans to feed its supervisory experience into the European Commission’s MiCA review, expected by June 2027, and prepare for any legislative proposal that may follow.Related: ECB, EU cenbanks seek changes in MiCA’s minimum bank deposit for stablecoinsCointelegraph is committed to independent, transparent journalism. This news article is produced in accordance with Cointelegraph’s Editorial Policy and aims to provide accurate and timely information. Readers are encouraged to verify information independently.

Čítaj viac
Bitget resumes Bitcoin withdrawals as hacker swaps ETH via THORChain

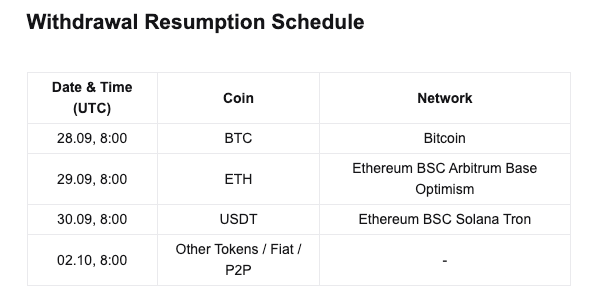
Crypto exchange Bitget is resuming withdrawals after a security breach affecting nearly $388 million in assets, as the attacker continues moving stolen crypto through THORChain.Bitget said it resumed Bitcoin (BTC) withdrawals Monday after suspending them following last week’s security incident, with additional assets and networks set to follow over the coming days.The Sept. 24 breach compromised part of Bitget’s hot and warm wallet infrastructure, while its cold wallets remained secure, according to the exchange. Bitget later revised the stolen amount from $351.6 million to $387.5 million after accounting for additional transfers on Zcash and Tron.Ether and USDT withdrawals next as security checks progressBTC withdrawals on the Bitcoin network and the BNB Smart Chain resumed first, Bitget CEO Gracy Chen said during a Monday ask-me-anything session.“We restored BTC first because the withdrawal pipeline is the first to be completed,” Chen said, adding that Ether (ETH) and Tether’s USDt (USDT) would follow as security checks progress.Related: Bitget clarifies $388M in assets affected by security breachUnder Bitget’s announced schedule, ETH withdrawals are set to resume Tuesday across Ethereum, BNB Smart Chain, Arbitrum, Base and Optimism, followed by USDT on Wednesday across Ethereum, BNB Smart Chain, Solana and Tron. Withdrawals for other assets and peer-to-peer services are scheduled to return Friday.Source: BitgetThe schedule applies to all users, with no priority access for institutions, VIP customers or Bitget employees, Chen said.THORChain says network halt cannot selectively freeze fundsBitget CEO Gracy Chen has called on THORChain, a decentralized protocol for swapping assets between blockchains, to refuse services to addresses linked to the attack.Lookonchain reported Monday that the attacker was swapping Ether for Bitcoin through THORChain, as Arkham data showed ETH linked to the attacker flowing into THORChain vaults.THORChain said Monday that its network halt is an emergency security mechanism that affects the protocol broadly and “is not a selective freeze of specific funds or an individual swap.”Source: ArkhamCrypto author Anndy Lian said THORChain can halt trading, stop outbound transactions or pause a connected chain, but those measures affect users broadly. The protocol has no built-in address blacklist, he said, limiting its ability to block specific addresses.Magazine: THORChain under fire over Bitget, ETH evolves beyond blockchain: Hodler’s Digest

Čítaj viac

SlowMist has yet to confirm crypto theft from iPhone Safari attack

An iPhone Safari attack behind recent security warnings hasn’t yet been linked to a confirmed cryptocurrency theft in SlowMist’s investigation.Multiple reports surfaced this week urging iPhone users to update their devices immediately and warning that malicious Safari pages could expose crypto private keys and seed phrases, with some citing a range from iOS 13 through iOS 26.5.SlowMist told Cointelegraph that it has not independently confirmed a victim compromised by the specific Safari attack sample it analyzed, while its strongest technical evidence covers iOS 18.4 through 18.6.2.The company said the “iOS 13 to 26.5” range should be treated as preliminary. “We therefore prefer to avoid stating that iOS 26.5 is affected until there is reproducible technical evidence,” it said.The Safari attack reuses techniques from a previously disclosed DarkSword exploit chain and is separate from FomoPeek, another SlowMist investigation involving malicious components embedded in an App Store app.SlowMist finds DarkSword reuseGoogle Threat Intelligence Group (GTIG) disclosed DarkSword in March, describing it as an iOS exploit chain that had been used by multiple threat actors since at least November 2025.SlowMist said MistEye, a threat intelligence team led by its chief information security officer, 23pds, first identified the relevant activity in early May.SlowMist published its analysis of the WYINCC Safari campaign on Sept. 4, identifying a malicious webpage advertising a free virtual private server service.SlowMist said the page loaded the exploit code when opened on an iPhone using Safari, without necessarily requiring another click from the user.The vulnerabilities used in the chain had already been disclosed and patched by Apple, SlowMist said.What the Safari attack was designed to accessSlowMist found that the malicious Safari sample it analyzed included a component designed to access Apple’s Keychain and retrieve and decrypt information stored there. The code could also access app files and shared app data, potentially exposing information stored by crypto wallet applications.“The sample demonstrates the collection capability and the intended targets; it does not by itself prove successful extraction from every targeted wallet,” SlowMist said.Related: EU watchdogs warn quantum computers could pick crypto’s locks“We did not execute the full chain on a real victim device, so we cannot identify a specific victim whose device we independently confirmed was successfully compromised by this exact sample,” SlowMist added.SlowMist still recommends updating iOSDespite the limits of the available evidence, SlowMist advised iPhone users to install the latest iOS security updates available for their devices and avoid suspicious links.For users who cannot update immediately or face elevated risks, SlowMist recommended considering Apple’s Lockdown Mode as an additional defense, while cautioning that it has not confirmed the feature completely blocks this specific Safari attack.SlowMist also urged users who believe a wallet key or seed phrase may have been exposed to move their assets to a newly generated wallet on a clean device rather than continue using potentially compromised credentials.Magazine: Asia dominates Crypto Adoption Index, Bitget’s $352M hack: Asia Express

Čítaj viac

Získaj BONUS 8 € v Bitcoinoch

nakup bitcoin z karty

Registrácia Binance

Burza Binance

Aktuálne kurzy